
By Abbinaya Kuzhanthaivel
As enterprises expand across multi-cloud infrastructure, hybrid data environments and connected systems, the challenge for security teams is no longer just identifying external threats. Knowing what is happening inside the enterprise and connecting activity across systems is becoming equally important.
Fragmented data, duplicated information and inconsistent security controls can create blind spots that make it harder to detect suspicious activity, investigate incidents and respond before threats spread.
In conversation with Tech Arabia, Nick Loumakis, Regional Vice President, The Middle East and Türkiye at Cloudera, shares insights on the growing visibility challenge and how organisations can strengthen security across distributed environments.
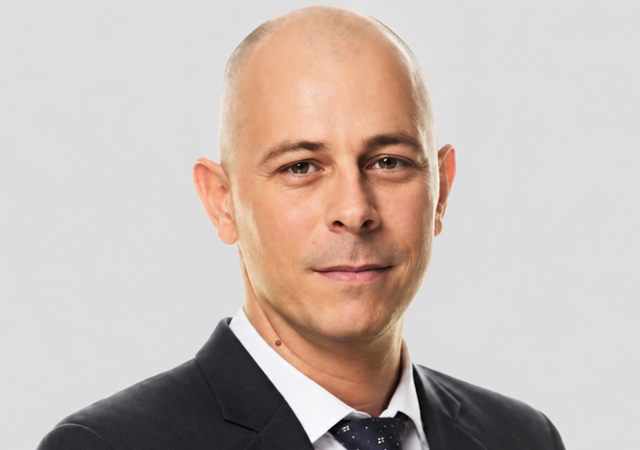
Nick Loumakis
Loumakis says the expansion of enterprise infrastructure has fundamentally changed the cybersecurity challenge, with organisations now operating across multi-cloud environments, hybrid data architectures and connected edge devices.
“Cybersecurity has fundamentally evolved from a threat problem into a visibility problem because modern organisations simply cannot defend digital assets or operational infrastructure they cannot clearly see,” he adds.
The first step is therefore to bring security information together and continuously analyse it across the technology environment. System logs, device activity and other security information can give security teams greater context about what is happening across connected endpoints.
For large enterprises, bringing this information together can help teams identify suspicious activity earlier, connect related events and reduce investigation time.
Data movement creates new gaps
The same visibility challenge applies to enterprise data. As information moves between cloud platforms, on-premise data centres and connected devices, it can be copied across systems and subjected to different access rules. Loumakis said the issue is not necessarily the data itself, but what happens to it as it moves between systems.
“As organisations move information across cloud platforms, on premises data centers, and connected devices, it can become fragmented, copied across multiple systems, and governed by inconsistent access rules.”
Repeatedly moving or duplicating sensitive information can reduce visibility and increase exposure to security and compliance risks. Loumakis says enterprises should instead focus on governing data where it resides. A unified data architecture, centralised security policies and automated data lineage can give organisations more control over how information is accessed and moved between systems.
Controls such as row-level filtering and dynamic column masking can also allow organisations to apply more granular protection to sensitive information.
Modernisation can add complexity
The move towards modern infrastructure can itself introduce security challenges when organisations deploy separate tools and policies across different platforms.
“Modernisation efforts often unintentionally create massive security complexity when enterprises deploy disjointed, platform-specific security tools across their expanding environments,” he explains.
According to Loumakis, redundant data copies and siloed access controls can turn digital transformation into an operational security risk.
Cloudera empowers businesses to assert control over 100% of their data
Managing separate policies across cloud providers, on-premise systems and analytics engines can also make it harder to maintain a consistent security posture.
Centralising security policies can help organisations define access rules once and apply them across different systems and workloads. Open data formats such as Apache Iceberg can further support data sharing without requiring unnecessary copies, while data lineage can show how information moves between environments.
Looking inside the enterprise
As enterprises become more distributed, perimeter protection alone cannot show what is happening inside the organisation. “Internal visibility and real-time information are critical, as attackers can move through an organization without relying on traditional network entry points,” Loumakis says.
An attacker gaining access through a compromised identity, endpoint or vulnerability may subsequently move across connected environments. If monitoring and access controls are managed separately, security teams may struggle to see that movement as it develops.
For organisations managing more than 130,000 endpoints across multiple cloud platforms, Loumakis says processing information as it happens can help shorten response times and give teams a clearer picture of activity across their environments.
The Barriers
The challenge is not collecting more security information. Enterprises already generate large volumes of logs, alerts and data from devices, firewalls and cloud systems. When that information is spread across isolated systems, however, security teams can struggle to determine what matters.
Loumakis identified architectural fragmentation and processing latency as barriers to turning this information into actionable threat intelligence.
Security teams need to analyse live data at its source rather than rely on delayed processing and repeated data movement.
Real-time ingestion, data lineage and unified access controls can help teams investigate security events faster.
AI raises the stakes
The security challenge becomes more acute as AI increases the speed and scale of cyberattacks.
Loumakis says AI is increasing the speed and scale at which cyberattacks can be carried out, while defensive AI remains constrained by fragmented data.
He adds that AI security tools depend heavily on the quality and availability of the data they receive. When security information is separated across cloud and on-premise environments, AI models may only see part of the information needed to identify suspicious behaviour.
Bringing security data together in real time can give AI systems more information about where data originates and how events are connected. That can help teams identify suspicious behaviour earlier and investigate it with more complete information.
From perimeter defence to cyber resilience
For Gulf organisations operating across these environments, a compromised identity or endpoint can become a wider security concern when access policies and monitoring are managed separately.
Centralised access policies, role-based controls, data-level restrictions and continuous monitoring can help organisations identify unusual activity and restrict access before an incident spreads to more sensitive systems.